Essential Standards and Frameworks for Westfield Business Cybersecurity Audits
Cyber threats are no longer just a risk for multinational corporations; they are a daily reality for local enterprises. According to recent industry data, small and medium-sized businesses are targeted in over 43% of all cyberattacks, with many of these incidents originating from automated scans and targeted phishing campaigns. For business owners in Westfield, Indiana, understanding the specific standards that protect your digital assets is not just a technical requirement but a fundamental component of operational continuity. This guide outlines the critical frameworks, audit procedures, and compliance standards that define modern cybersecurity posture. (Contact Us for IT)
Understanding the NIST Cybersecurity Framework
The National Institute of Standards and Technology (NIST) has established a framework that serves as the gold standard for managing cybersecurity risk. NIST CSF is a policy framework of computer security guidance. It provides a high-level, strategic view of the status of an organization's cybersecurity risk management. For businesses in Westfield, adopting this framework means aligning their security practices with nationally recognized benchmarks. (About Maranatha Tech Solutions)
The framework is built on five core functions: Identify, Protect, Detect, Respond, and Recover. Each function addresses a specific phase of cybersecurity management. The Identify function focuses on understanding the business context and the resources that need protection. This includes asset management, governance, and risk assessment. Without a clear inventory of hardware and software, a business cannot effectively secure its environment. (Custom Software Web amp)
The Protect function outlines the safeguards necessary to ensure delivery of critical services. This includes access control, awareness training, and data security. For many Westfield businesses, the gap between current practices and NIST standards lies in employee training and data encryption protocols. Implementing these safeguards requires a shift from reactive security measures to proactive risk management.
Detect, Respond, and Recover functions focus on the operational aspects of security. Detect involves the development and implementation of appropriate activities to identify the occurrence of a cybersecurity event. Response is about the development and implementation of appropriate activities to take action regarding a detected cybersecurity incident. Recovery focuses on maintaining plans for resilience and restoring any systems or services that were impaired due to a cybersecurity incident. NIST guidelines emphasize that these functions are not linear but iterative, requiring continuous improvement.
ISO 27001 and International Compliance
While NIST is widely used in the United States, the International Organization for Standardization (ISO) provides a globally recognized framework for information security management systems (ISMS). ISO 27001 is the international standard for information security. It specifies the requirements for establishing, implementing, maintaining, and continually improving an information security management system.
For Westfield businesses that operate in global markets or work with international clients, ISO 27001 certification can be a competitive advantage. It demonstrates to partners and customers that the business takes data protection seriously. The standard requires a risk-based approach to information security, ensuring that resources are allocated to the most significant threats.
Implementing ISO 27001 involves several key steps. First, the scope of the ISMS must be defined. This includes identifying the boundaries and applicability of the system. Next, a risk assessment must be conducted to identify potential threats and vulnerabilities. Based on this assessment, a risk treatment plan is developed to mitigate identified risks. The implementation phase involves putting controls in place, such as access controls, cryptography, and physical security measures.
Regular internal audits and management reviews are essential components of ISO 27001 compliance. These reviews ensure that the ISMS remains suitable, adequate, and effective. ISO 27001 standards also require continual improvement, meaning that businesses must regularly update their security practices to address emerging threats and changes in the business environment.
Regulatory Requirements: GDPR and HIPAA
Depending on the nature of their operations, Westfield businesses may be subject to specific regulatory requirements. The General Data Protection Regulation (GDPR) applies to any organization that processes the personal data of individuals in the European Union. GDPR is a regulation in EU law on data protection and privacy. It sets strict guidelines for the collection and processing of personal information, including how companies obtain consent, how they store data, and how they protect it.
For businesses handling healthcare information, the Health Insurance Portability and Accountability Act (HIPAA) is the primary regulatory framework. HIPAA sets national standards for the protection of sensitive patient data. It requires covered entities to implement administrative, physical, and technical safeguards to ensure the confidentiality, integrity, and availability of electronic protected health information (ePHI).
Compliance with these regulations is not optional. Violations can result in significant fines and reputational damage. For example, GDPR fines can reach up to 20 million euros or 4% of global annual turnover, whichever is higher. HIPAA violations can result in penalties ranging from $100 to $50,000 per violation, with a maximum penalty of $1.5 million per year for identical provisions.
Westfield businesses must conduct regular compliance audits to ensure they are meeting these regulatory requirements. This includes reviewing data processing agreements, conducting risk assessments, and implementing appropriate technical controls. FTC guidelines also emphasize the importance of reasonable security measures to protect consumer data.
The Cybersecurity Audit Process
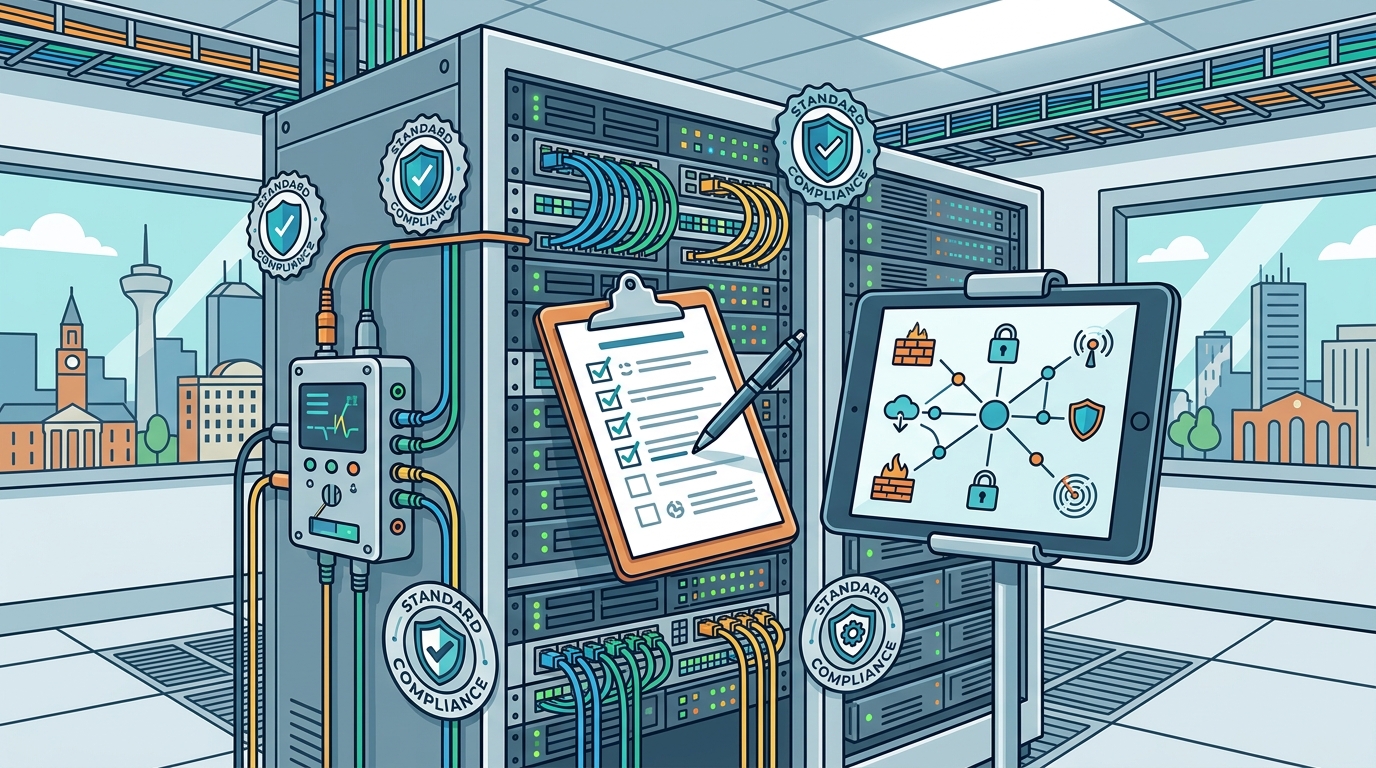
A cybersecurity audit is a systematic evaluation of the security posture of an organization. It involves reviewing the organization's information systems, policies, and procedures to identify vulnerabilities and ensure compliance with established standards. The audit process typically includes several phases: planning, fieldwork, reporting, and follow-up.
During the planning phase, the scope and objectives of the audit are defined. This includes identifying the assets to be audited, the standards to be used for evaluation, and the resources required. The fieldwork phase involves collecting evidence through interviews, observations, and technical testing. This may include vulnerability scanning, penetration testing, and configuration reviews.
The reporting phase involves documenting the findings of the audit, including identified vulnerabilities, compliance gaps, and recommendations for improvement. The report should be clear, concise, and actionable. The follow-up phase involves monitoring the implementation of recommended changes and verifying that they effectively mitigate the identified risks.
For Westfield businesses, regular audits are essential for maintaining a strong security posture. They help identify weaknesses before they can be exploited by attackers. SANS Institute recommends that businesses conduct audits at least annually, or more frequently if there are significant changes to the IT infrastructure.
Choosing a Cybersecurity Partner
Implementing and maintaining a robust cybersecurity program requires specialized expertise. Westfield businesses should look for partners who understand both the technical aspects of security and the specific needs of local enterprises. Key factors to consider include experience, certifications, and service offerings.
Experience is critical. A partner with a proven track record in implementing NIST, ISO, and other frameworks will be better equipped to guide your business through the complexities of compliance. Certifications such as CISSP, CISM, and CISA demonstrate a professional's commitment to security best practices.
Service offerings should align with your business needs. This may include managed security services, penetration testing, compliance consulting, and incident response planning. A comprehensive partner will offer end-to-end support, from initial assessment to ongoing monitoring and improvement.
Maranatha Tech Solutions provides enterprise-level engineering experience tailored to the needs of Westfield businesses. Our approach combines technical expertise with a commitment to integrity and excellence. We help businesses implement robust security frameworks, from custom software development to AI automation. Explore our services to learn how we can support your cybersecurity goals.
Key Takeaways
- NIST CSF provides a strategic framework for managing cybersecurity risk through five core functions: Identify, Protect, Detect, Respond, and Recover.
- ISO 27001 is the international standard for information security management systems, offering a globally recognized benchmark for compliance.
- GDPR and HIPAA impose strict regulatory requirements on data protection, with significant penalties for non-compliance.
- Cybersecurity audits are essential for identifying vulnerabilities and ensuring ongoing compliance with established standards.
- Partner selection should be based on experience, certifications, and a comprehensive range of security services.
- Maranatha Tech Solutions offers enterprise-grade engineering and AI automation to enhance Westfield business security.
- Continuous improvement is key to maintaining a strong security posture in the face of evolving threats.
Frequently Asked Questions
What is the most important cybersecurity standard for Westfield businesses?
While the NIST Cybersecurity Framework is widely adopted in the United States, the most important standard depends on your specific industry and client base. For global operations, ISO 27001 may be more relevant. For healthcare, HIPAA is mandatory. For EU data processing, GDPR applies.
How often should a business conduct a cybersecurity audit?
Best practices recommend conducting a comprehensive cybersecurity audit at least annually. However, audits should also be performed after significant changes to the IT infrastructure, following a security incident, or when new regulations come into effect.
What is the difference between a vulnerability assessment and a penetration test?
A vulnerability assessment identifies and quantifies vulnerabilities in a system, while a penetration test actively attempts to exploit those vulnerabilities to determine the potential impact. Both are essential components of a robust security audit.
Can small businesses afford comprehensive cybersecurity compliance?
Yes. While compliance can be costly, the cost of a data breach is significantly higher. Many frameworks, such as NIST CSF, are scalable and can be implemented in phases based on budget and risk profile.
What role does AI play in cybersecurity audits?
AI and machine learning are increasingly used to analyze large volumes of security data, identify anomalies, and automate threat detection. This enhances the efficiency and accuracy of cybersecurity audits.
How does Maranatha Tech Solutions approach cybersecurity?
We combine enterprise-level engineering experience with a values-driven partnership. We help businesses implement custom security solutions, from network architecture to AI-driven threat detection, ensuring compliance and resilience.
What is the first step in improving cybersecurity posture?
The first step is to conduct a thorough risk assessment and asset inventory. You cannot protect what you do not know you have. This foundational work enables the development of a targeted security strategy.
Secure Your Business Today
Cybersecurity is not a one-time project but an ongoing commitment to protecting your business and your customers. Westfield businesses must stay vigilant and proactive in the face of evolving threats. By adopting established frameworks like NIST and ISO, and partnering with experienced professionals, you can build a resilient security posture.
Maranatha Tech Solutions is ready to help you navigate the complexities of cybersecurity. From custom software development to AI automation, we provide the expertise you need to safeguard your digital assets. Schedule a consultation today to discuss your specific needs and develop a tailored security strategy.